

Researchers from the Netherlands and Italy have unveiled a new attack that expands the Spectre-v2 class of vulnerabilities. Unlike the original 2018 attack, which relied on branch target injection, this new method utilizes Branch Target Reuse within the processor's branch prediction system. The vulnerability is triggered by interactions with JIT compilers, a scenario previously considered impractical. The study successfully demonstrated the extraction of secret data via the cBPF JIT compiler in the Linux kernel. Experts also analyzed potential risks for the SpiderMonkey (Firefox) and GraalVM compilers. This research highlights the need to re-evaluate security approaches for branch prediction mechanisms in modern processors, as the combination of JIT compilation features and hardware optimizations creates new vectors for side-channel attacks.
This is a summary. Read the full article at the original source:
HabrRelated stories

Vulnerabilities in Model Context Protocol expose risks in AI agent communication
Independent researcher Syed Anas Mohiuddin has identified critical security flaws in the Model Context Protocol (MCP), a standard used for communicati…

A new Linux-based backdoor, dubbed ClingSTUN, is actively targeting vulnerable Internet of Things (IoT) devices to transform them into proxy nodes. Ac…
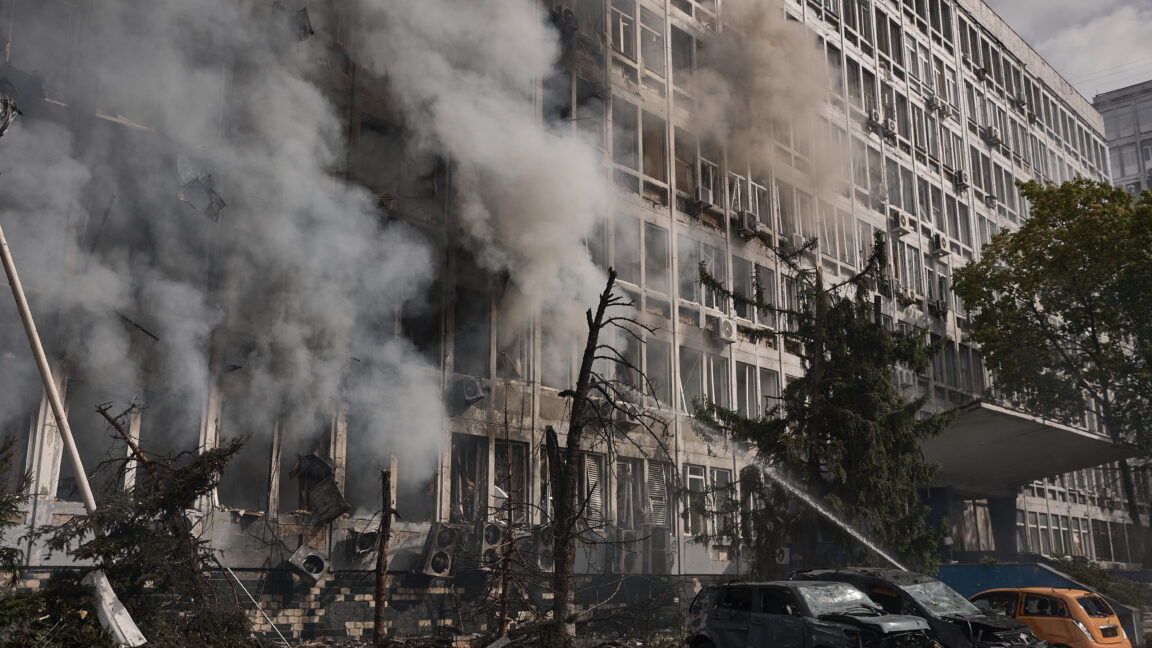
Russian drone strikes target Ukrainian data centers and telecom infrastructure
A recent escalation in Russian jet-powered drone strikes has specifically targeted data centers and telecommunications infrastructure in Kyiv, causing…