

A new Linux-based backdoor, dubbed ClingSTUN, is actively targeting vulnerable Internet of Things (IoT) devices to transform them into proxy nodes. According to researchers, the malware exploits 24 known security vulnerabilities to gain unauthorized access to hardware. Once compromised, these devices are used to route malicious traffic, effectively masking the origin of cyberattacks. A key feature of ClingSTUN is its use of legitimate public STUN (Session Traversal Utilities for NAT) servers to facilitate communication and obscure its command-and-control infrastructure. By leveraging these standard network protocols, the attackers make it significantly harder for security teams to detect and block the malicious activity. The discovery highlights the persistent risks associated with unpatched IoT hardware and the creative methods threat actors employ to maintain persistence within compromised networks. Security experts urge users to update firmware and implement robust network monitoring to mitigate the threat posed by this sophisticated backdoor.
This is a summary. Read the full article at the original source:
Dark ReadingRelated stories
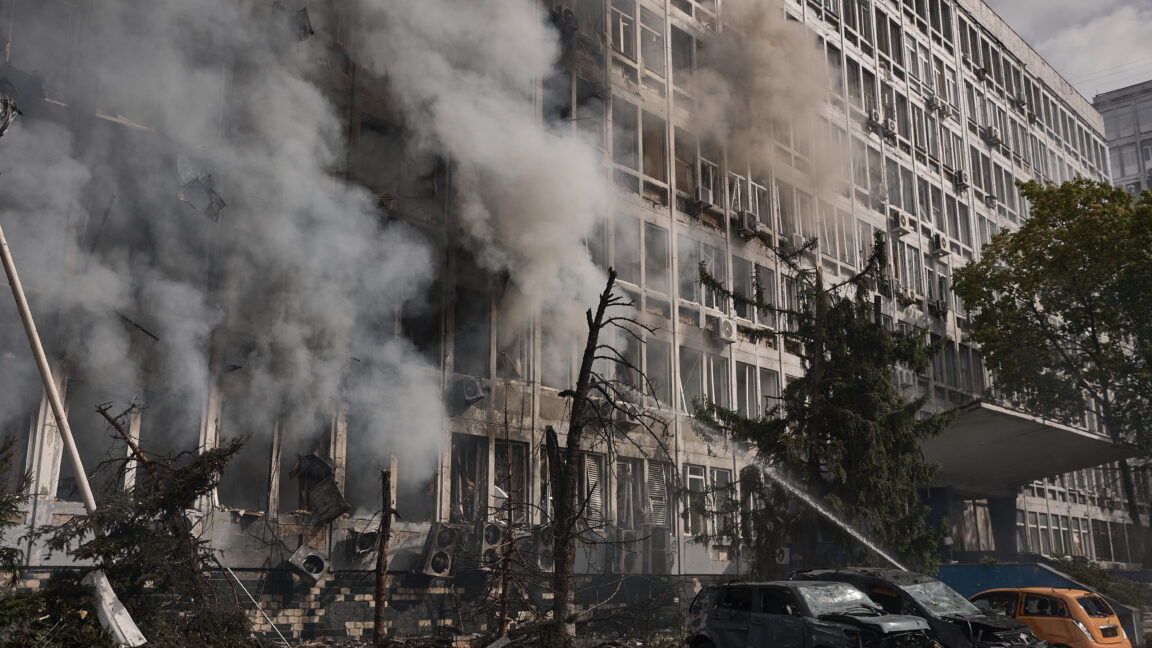
Russian drone strikes target Ukrainian data centers and telecom infrastructure
A recent escalation in Russian jet-powered drone strikes has specifically targeted data centers and telecommunications infrastructure in Kyiv, causing…
A newly identified threat group, designated as TA419, has been observed conducting sophisticated cyber espionage campaigns targeting AI policy experts…
The GrapheneOS project has indicated that the upcoming Google Pixel 11 series may not be supported by their privacy-focused operating system. Accordin…