
Deception by Design: CISA's Guide to Tricking Cybercriminals
The Cybersecurity and Infrastructure Security Agency (CISA) has released a new guide aimed at helping organizations with limited resources implement deception technologies to defend against cyber threats. By using 'deception by design,' companies can deploy traps, decoys, and honeytokens to detect and confuse attackers early in the intrusion process. The agency emphasizes that these strategies do not require massive budgets or complex infrastructure, making them accessible to smaller entities. The guide outlines how to integrate these deceptive elements into existing network architectures to increase the cost of attacks for malicious actors. By forcing adversaries to interact with fake assets, security teams can gain valuable insights into attacker tactics, techniques, and procedures (TTPs) while simultaneously slowing down their progress. This initiative marks a strategic shift toward proactive defense, encouraging organizations to move beyond traditional perimeter security and adopt more resilient, trap-based defensive postures.
This is a summary. Read the full article at the original source:
Dark ReadingRelated stories
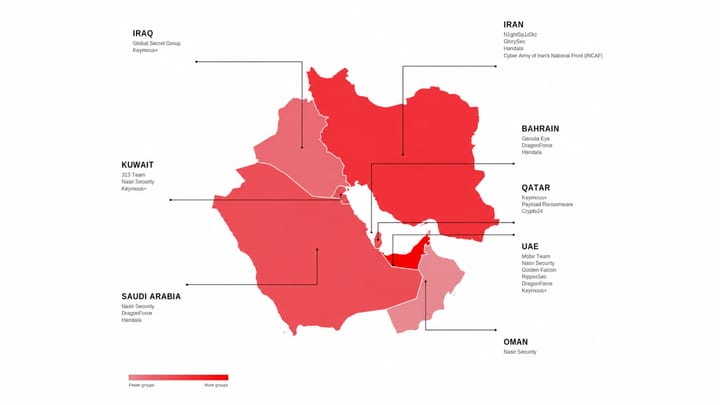
A recent report from Dark Reading highlights a significant escalation in the cyber threat landscape across the Gulf region. During the first half of 2…
Attackers Manipulate AI Chatbots in Mass Disinformation and Phishing Campaign
Threat actors are increasingly targeting generative AI platforms, including ChatGPT, Gemini, and Google AI Overview, to conduct large-scale disinforma…

Meta has addressed a critical zero-day vulnerability discovered in its Muse AI assistant, a tool designed to streamline workflows for Mac users. Secur…