
Meta’s Muse AI Assistant Rolled Out With a Serious Security Flaw

Meta has addressed a critical zero-day vulnerability discovered in its Muse AI assistant, a tool designed to streamline workflows for Mac users. Security researchers identified that the flaw could have granted attackers unauthorized control over a victim's machine, allowing them to execute arbitrary commands and perform malicious actions. The vulnerability underscores the growing security risks associated with the rapid integration of AI agents into local operating environments. While Meta confirmed that a patch has been issued to resolve the issue, the incident serves as a stark reminder of the potential dangers posed by AI helpers that require deep system access. As companies continue to deploy autonomous AI assistants, the balance between user convenience and robust security remains a significant challenge for developers and users alike.
This is a summary. Read the full article at the original source:
WiredRelated stories
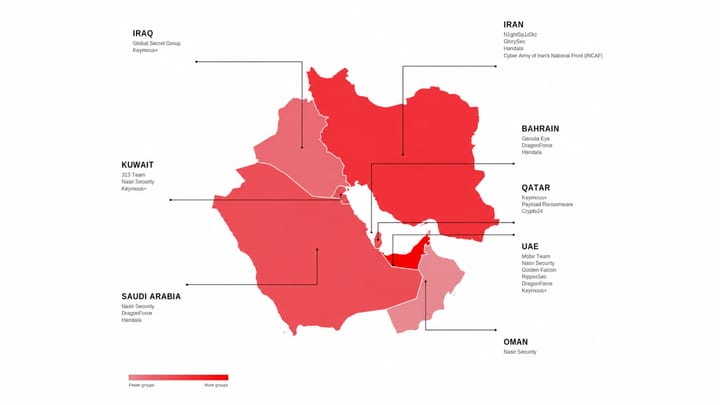
A recent report from Dark Reading highlights a significant escalation in the cyber threat landscape across the Gulf region. During the first half of 2…
Attackers Manipulate AI Chatbots in Mass Disinformation and Phishing Campaign
Threat actors are increasingly targeting generative AI platforms, including ChatGPT, Gemini, and Google AI Overview, to conduct large-scale disinforma…

The rise of smart glasses in India is raising significant privacy and safety concerns, as these inconspicuous devices are increasingly used for non-co…