
Dangling pointer in HTTP/2 leads to RCE in curl: CVE-2026-92392 analysis by Stenberg
Curl version 8.23.0 has patched a use-after-free vulnerability occurring during HTTP/2 transfers. The flaw allowed a server to reset a stream, leaving a dangling pointer to an easy handle within libcurl. This enabled attackers to overwrite freed memory where a function pointer was stored, potentially leading to Remote Code Execution (RCE). Daniel Stenberg, the author of curl, provided a detailed breakdown of the attack chain and explained why the vulnerability was rated HIGH rather than CRITICAL. Notably, the bug was discovered by an AI-powered scanner from Anthropic. Stenberg also addressed questions regarding a potential rewrite of curl in Rust, highlighting the complexities involved in such a transition for a project of this scale. This incident underscores the ongoing necessity for rigorous security audits in fundamental networking libraries.
This is a summary. Read the full article at the original source:
HabrRelated stories
For 25 years, the origin of the seed values for the NIST P-192 through P-521 curves remained a mystery. Provided by the NSA without explanation, they…
Researchers uncover 'AdFection' zero-click spyware campaign delivered via online ads
Cybersecurity researchers at Citizen Lab have identified a sophisticated zero-click spyware campaign dubbed 'AdFection' that infects devices through m…
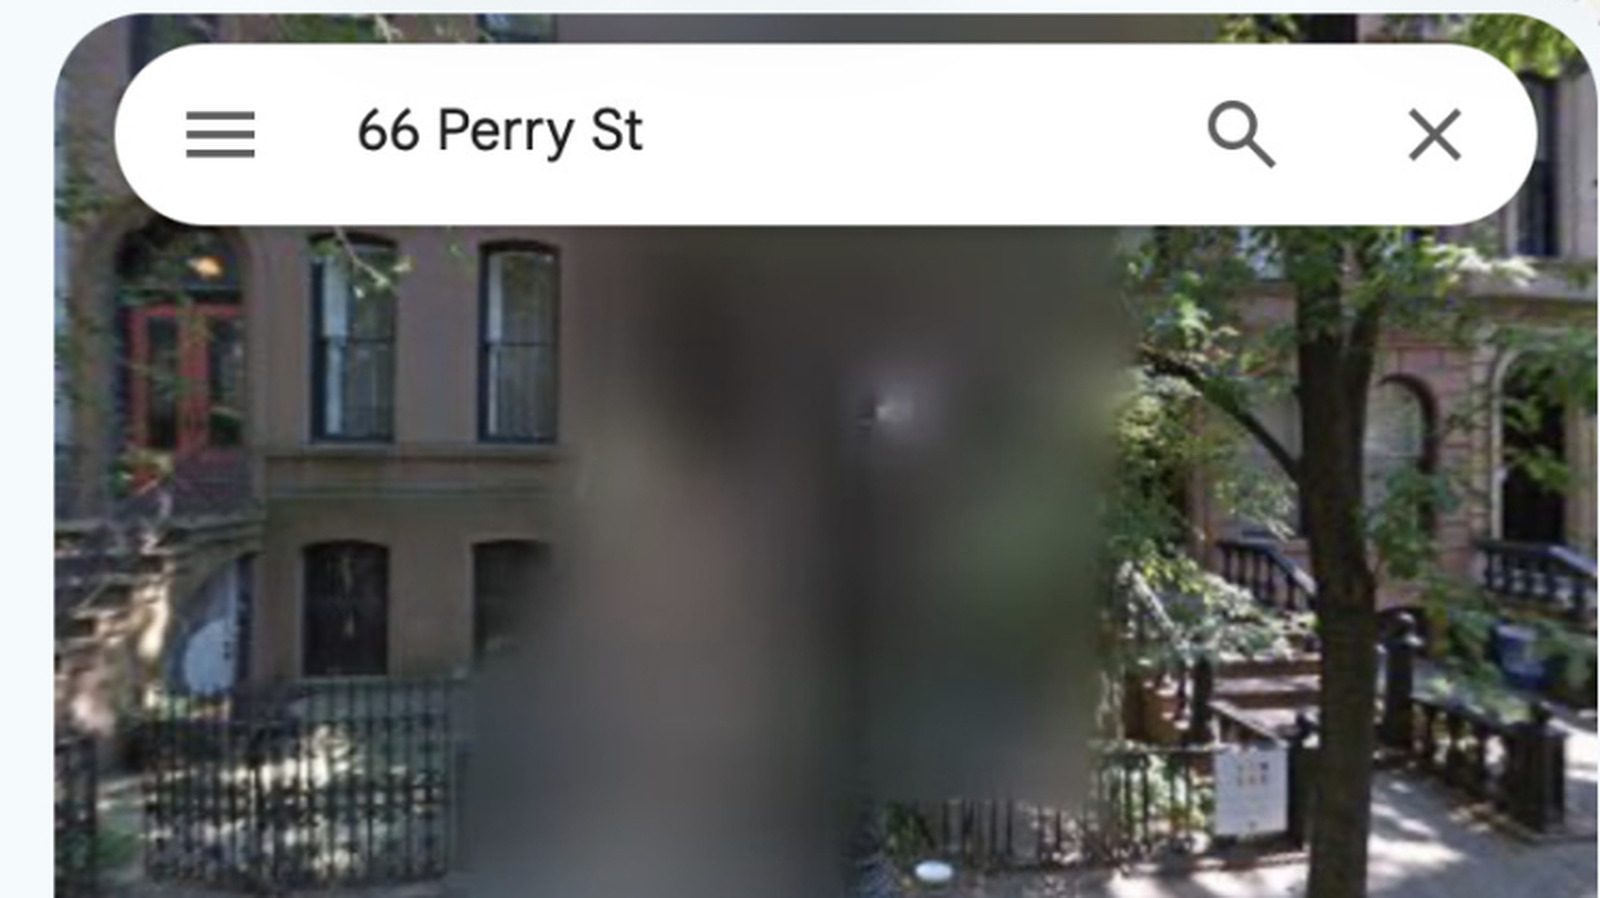
Users frequently encounter blurred-out areas while navigating Google Maps, a phenomenon that often sparks curiosity regarding the platform's mapping p…