
In open source cybersecurity, AI is both a challenge and a solution
At the Linux Foundation Open Source Summit, IBM's Jamie Thomas highlighted the growing crisis in open-source security, noting that vulnerability disclosures are expected to reach 66,000 by 2026. The industry faces a 'tsunami' of threats, with exploit times shrinking to as little as 29 minutes. While AI offers potential for defense, it is currently exacerbating the problem by enabling the mass generation of low-quality, duplicated, and fake vulnerability reports. Major projects, including curl and Google’s Open Source Software Vulnerability Rewards Program, have been forced to suspend bug bounty initiatives due to the unmanageable influx of AI-generated noise. Even Linux creator Linus Torvalds has criticized the impact of these automated tools on security mailing lists. As attackers leverage automation to accelerate their operations, the cybersecurity community must find a balance, utilizing AI for remediation while mitigating the overwhelming volume of false positives that threaten to paralyze open-source maintenance.
This is a summary. Read the full article at the original source:
TechRadarRelated stories

A recent security incident involving the British online retailer ASOS has highlighted the significant vulnerabilities associated with customer-facing…
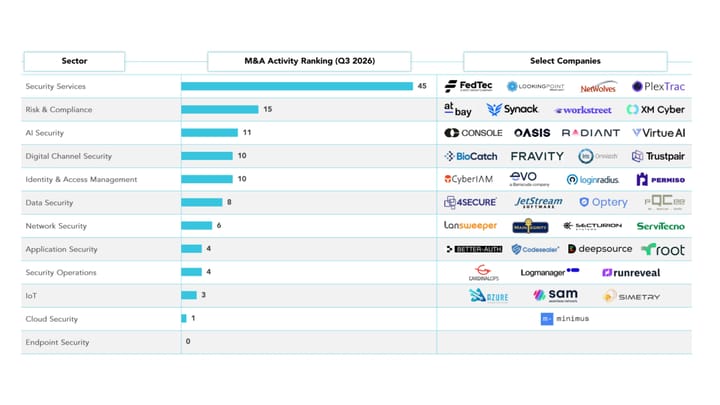
The cybersecurity sector is experiencing a significant surge in mergers and acquisitions, with 117 deals reported in the most recent quarter. Industry…
In a recent discussion, Dark Reading editors highlighted significant cybersecurity developments that recently emerged. A primary focus was the FBI's r…