

A recent security incident involving the British online retailer ASOS has highlighted the significant vulnerabilities associated with customer-facing Software-as-a-Service (SaaS) platforms. According to reports from Dark Reading, the breach demonstrates how attackers can exploit a single compromised identity to gain unauthorized access to broader corporate network segments. Security experts warn that as organizations increasingly rely on third-party SaaS applications for customer interactions, these platforms become high-value targets for cybercriminals. The incident serves as a critical reminder for enterprises to implement robust identity and access management (IAM) protocols, enforce multi-factor authentication, and conduct regular security audits of their SaaS ecosystem. By failing to secure these entry points, companies risk not only data exposure but also deep-level network infiltration that can lead to more severe operational disruptions. The ASOS case underscores the necessity of a zero-trust approach in modern digital business environments.
This is a summary. Read the full article at the original source:
Dark ReadingRelated stories
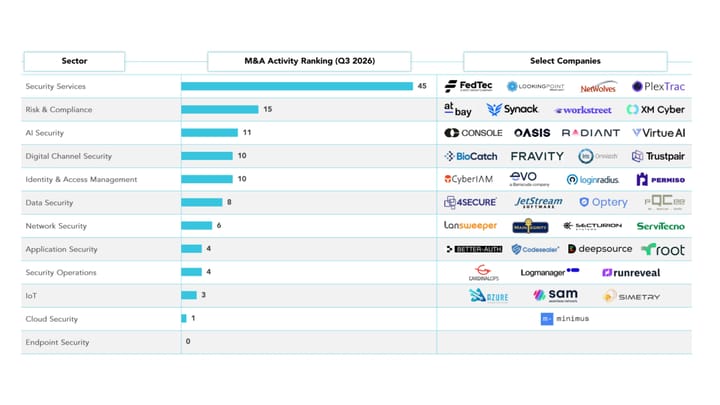
The cybersecurity sector is experiencing a significant surge in mergers and acquisitions, with 117 deals reported in the most recent quarter. Industry…
In a recent discussion, Dark Reading editors highlighted significant cybersecurity developments that recently emerged. A primary focus was the FBI's r…
Security Threats Don't Stop at the Office: Why Executives' Families Need Training, Too
A recent report from Dark Reading highlights a critical vulnerability in corporate security: the personal lives of high-level executives. As organizat…