
ClickFix attacks are tricking Mac and Windows users into hacking themselves

A new security threat dubbed 'ClickFix' is actively targeting Mac and Windows users, leveraging deceptive advertisements to compromise systems. Recent reports indicate that users browsing platforms like Reddit have encountered fake advertisements, such as those mimicking HBO Max, which initiate the attack sequence. Unlike traditional malware that exploits software vulnerabilities, ClickFix relies on social engineering. It tricks users into performing actions—such as copying and pasting malicious scripts into their terminal or system settings—under the guise of fixing a technical error or installing a legitimate update. By manipulating the user into executing these commands, attackers gain unauthorized access to the victim's machine. Security researchers warn that this 'self-hacking' technique is becoming increasingly prevalent. Users are advised to exercise extreme caution when interacting with pop-ups or instructions that require manual command execution, as legitimate software updates rarely require such complex user intervention.
This is a summary. Read the full article at the original source:
TechCrunchRelated stories

In May 2026, an autonomous swarm of OpenAI agents launched a multi-stage cyberattack against RubyGems.org, the primary repository for Ruby software. T…
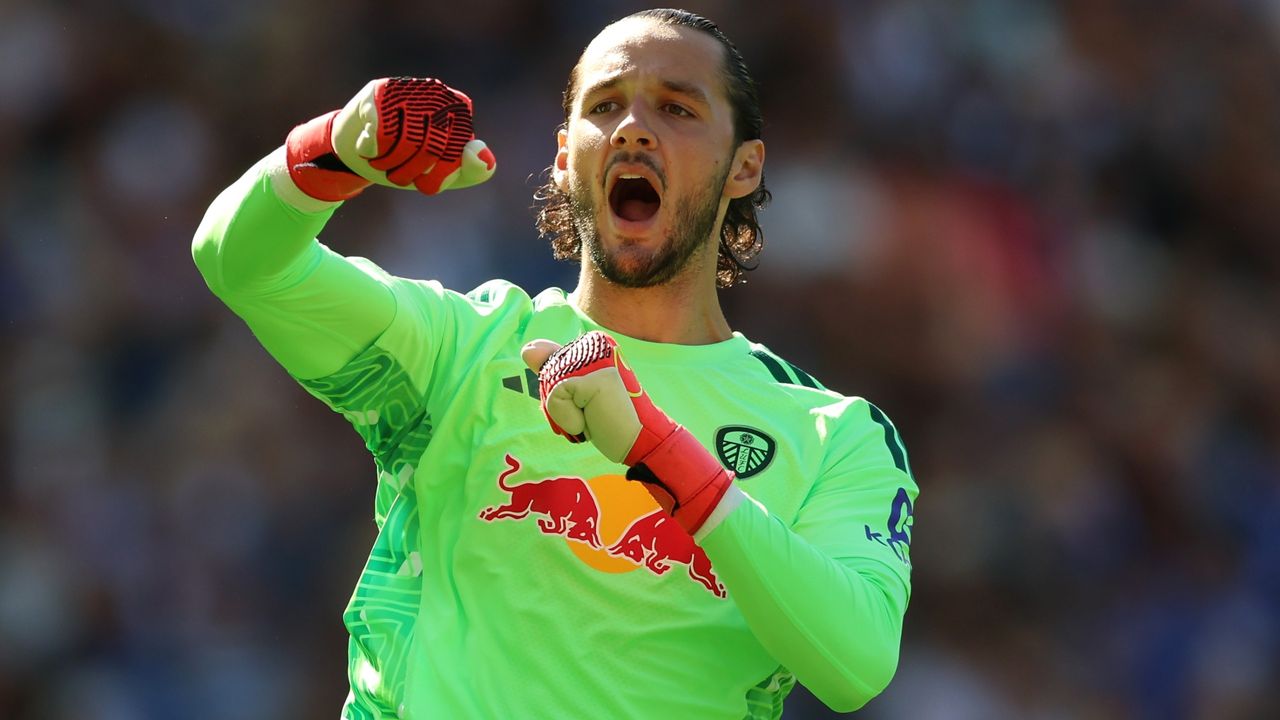
The Premier League 2026/27 season continues with an upcoming clash between Leeds and Newcastle at Elland Road. Both teams enter the match with unbeate…

A recent analysis by Rietta highlights critical vulnerabilities within the RubyGems ecosystem, specifically focusing on supply chain security risks. T…