

A recent analysis by Rietta highlights critical vulnerabilities within the RubyGems ecosystem, specifically focusing on supply chain security risks. The report details how malicious actors can exploit the open-source package management system to inject harmful code into downstream applications. A significant portion of the discussion centers on the intersection of these security threats with AI-driven tools like OpenAI, which are increasingly used to generate or review code. The author warns that while AI can assist developers, it may also inadvertently propagate insecure coding patterns or fail to detect sophisticated supply chain attacks. The article serves as a cautionary tale for the Ruby community, emphasizing the necessity of rigorous dependency auditing, the implementation of robust security protocols, and a heightened awareness of how automated tools interact with open-source repositories to maintain the integrity of the software supply chain.
This is a summary. Read the full article at the original source:
Hacker News (YC)Related stories
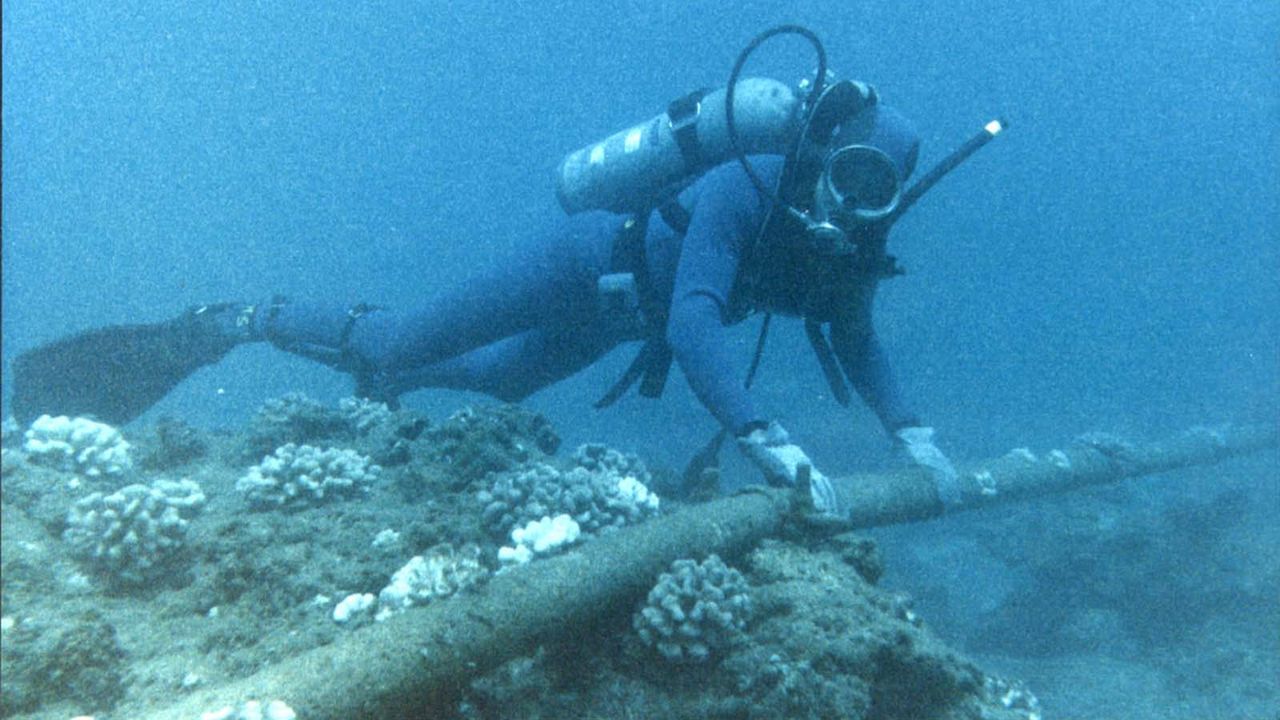
NATO Intercepts Russian Attempt to Test Stealthy Undersea Cable-Cutting Technology
NATO forces recently disrupted a Russian naval exercise near Svalbard after detecting preparations to test a specialized device capable of severing un…

Signal is advancing its privacy-focused mission by introducing a mechanism that allows users to register for the messaging service without relying on…

In 2003, researchers at the University of Wisconsin-Madison discovered a significant network issue caused by a flaw in Netgear routers. Thousands of t…