
Anthropic Launches AI-Powered OSS Scanner for Open-Source Security

Anthropic has introduced OSS Scanner, a free, opt-in service that utilizes its frontier AI models to identify vulnerabilities in open-source projects. Designed to assist maintainers, the tool provides automated reports containing a reproducer, an explanation of the issue, and, when possible, a suggested patch. The service focuses on projects with critical infrastructure or security implications. Anthropic emphasizes that these reports are entirely model-generated and lack human review, meaning maintainers must validate findings before implementation. While the tool aims to accelerate security testing, it is intended to complement, not replace, existing security practices and coordinated vulnerability disclosure processes. By providing actionable data, Anthropic hopes to help maintainers address potential flaws more efficiently, though the company warns that the accuracy of AI-generated outputs can vary. This initiative marks a significant step in integrating AI into the defensive security lifecycle for the broader open-source ecosystem.
This is a summary. Read the full article at the original source:
Dev.toRelated stories

A recent security incident involving the British online retailer ASOS has highlighted the significant vulnerabilities associated with customer-facing…
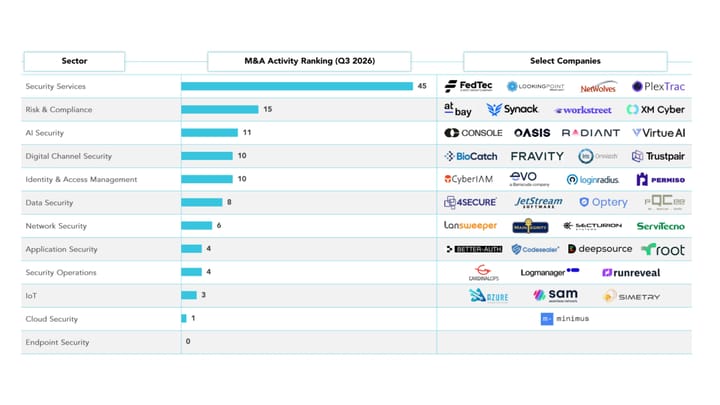
The cybersecurity sector is experiencing a significant surge in mergers and acquisitions, with 117 deals reported in the most recent quarter. Industry…
In a recent discussion, Dark Reading editors highlighted significant cybersecurity developments that recently emerged. A primary focus was the FBI's r…