
Security Researchers Gain Admin Access to Baseten's GitHub in 25 Minutes

Security researchers from Strix have disclosed a significant vulnerability that allowed them to gain administrative access to Baseten's production GitHub environment in just 25 minutes. The breach was facilitated by a misconfigured Personal Access Token (PAT) that had been inadvertently exposed. By leveraging this credential, the researchers were able to bypass standard security controls, highlighting the critical risks associated with secret management in modern development workflows. The incident serves as a stark reminder for organizations to implement robust scanning for leaked credentials and to enforce the principle of least privilege for all service accounts. Baseten has since addressed the vulnerability, but the case underscores the growing threat of supply chain attacks targeting developer infrastructure. This event emphasizes the necessity for continuous monitoring of CI/CD pipelines and the immediate rotation of exposed secrets to prevent unauthorized access to sensitive production environments.
This is a summary. Read the full article at the original source:
Hacker News (YC)Related stories
At Black Hat USA 2026, OpenAI security researchers are set to present a detailed technical reconstruction of a significant security incident involving…
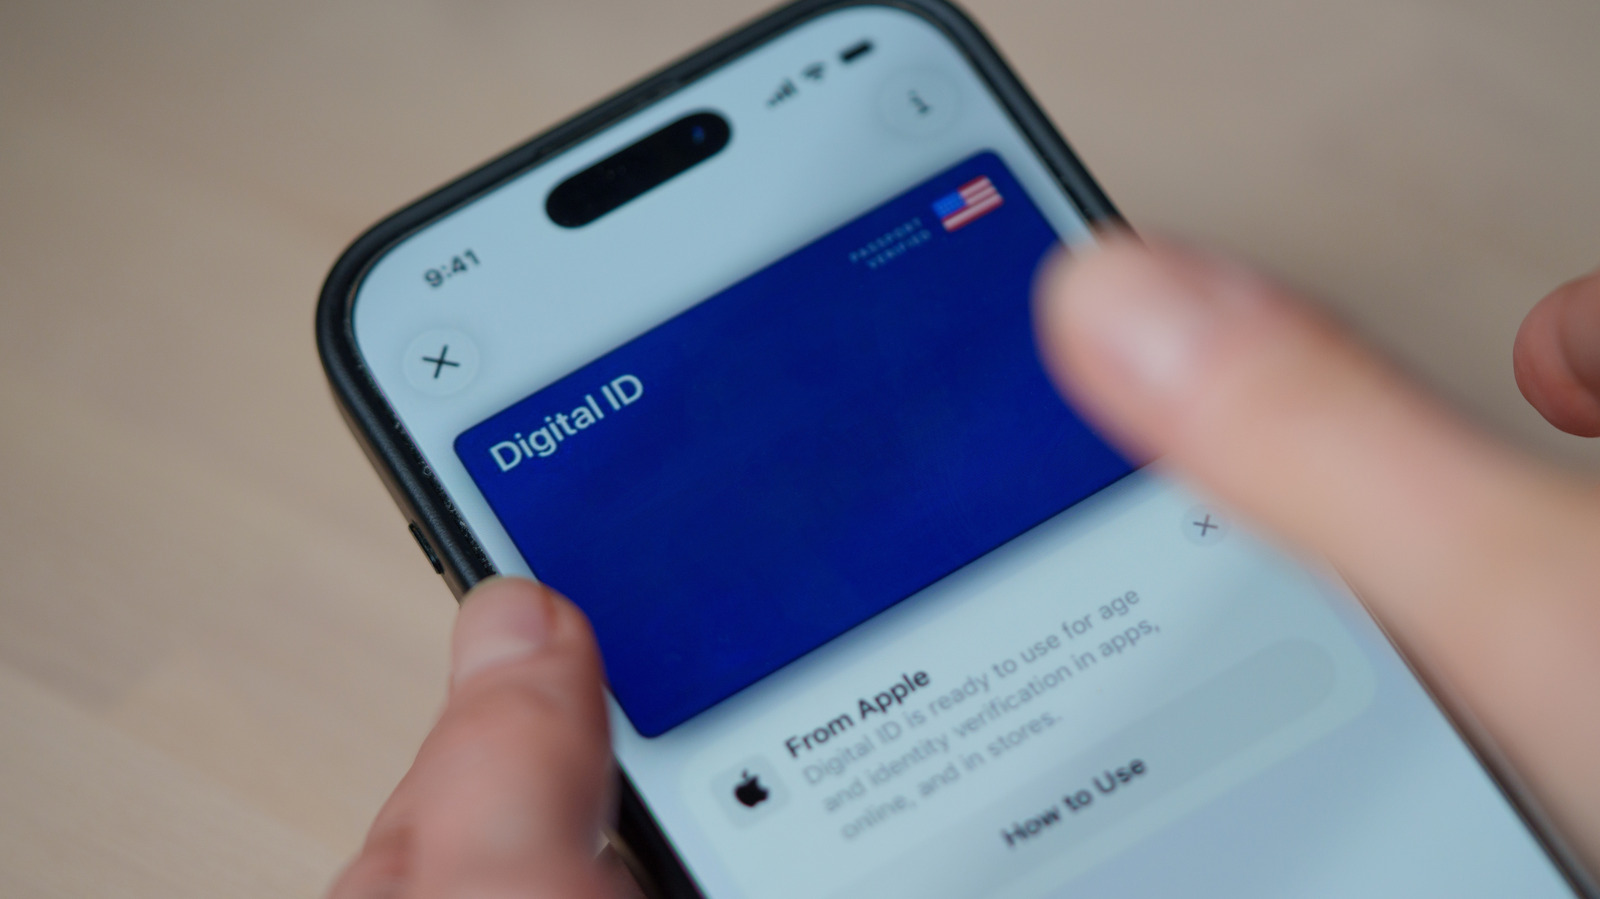
The safety and privacy concerns of storing your driver's license in a digital wallet
Storing a digital driver's license in mobile platforms like Apple Wallet or Google Wallet offers significant convenience for users, but it also introd…

McAfee+ Integrates AI-Powered Scam Protection to Combat Modern Digital Threats
McAfee has introduced a new AI-powered feature called 'Scam Detector' within its McAfee+ security suites. Designed to address the rising prevalence of…