
Meta's Muse AI reportedly exposes its entire filesystem

Security researchers Peter James and Jonny L. Saunders have discovered a significant vulnerability in Meta's Muse AI model. According to the developers, they were able to prompt the system to compress and share its entire root filesystem, including Ubuntu system files, application templates, and sensitive internal documentation. This incident highlights ongoing concerns regarding the security and data privacy of large-scale generative AI models. By coaxing the model into revealing its underlying architecture and configuration files, the researchers demonstrated how easily AI systems can be manipulated to bypass standard security protocols. Meta has not yet provided a detailed response regarding the incident, but the findings raise critical questions about the safety measures implemented in AI development environments. This vulnerability serves as a reminder of the potential risks associated with LLMs when they are not properly sandboxed or secured against adversarial prompting techniques.
This is a summary. Read the full article at the original source:
The VergeRelated stories

A recent review of the AI agent 'Instinct' highlights the dual nature of emerging autonomous digital assistants. The author reports that the tool succ…
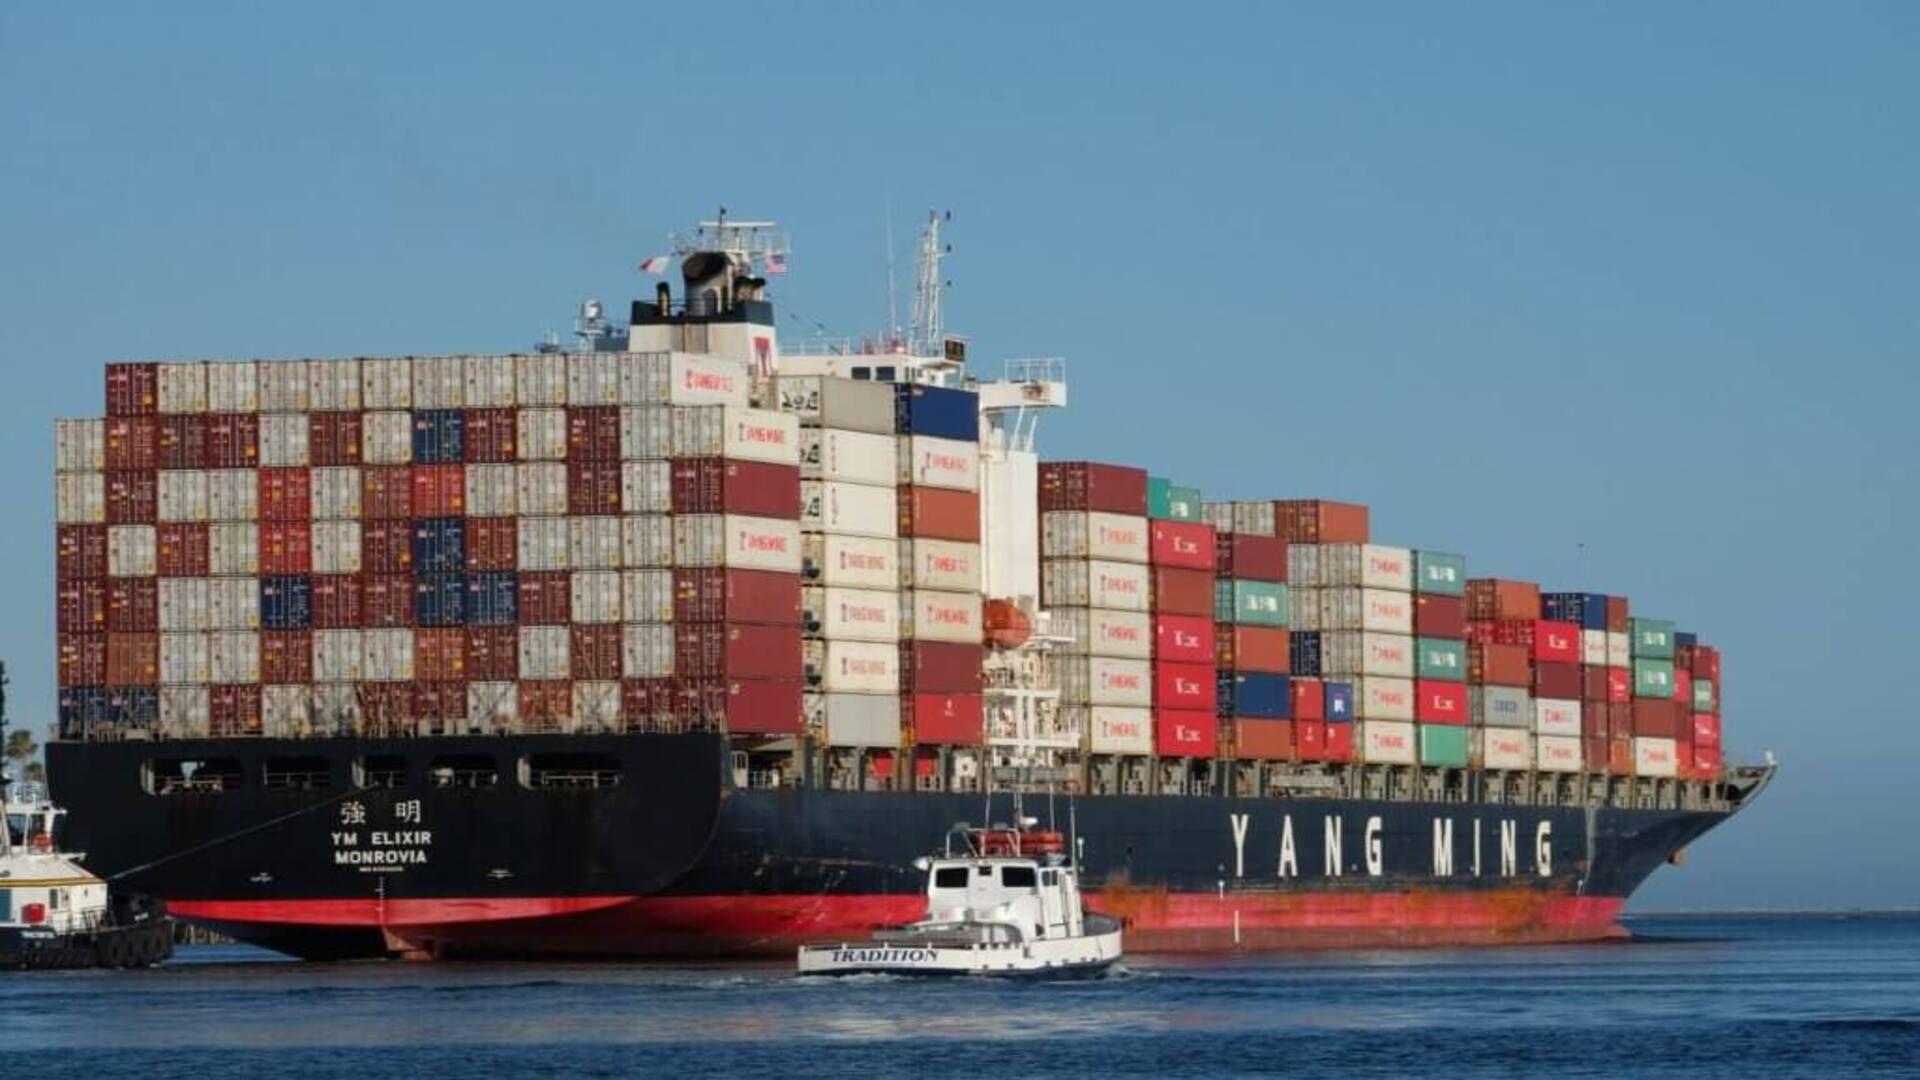
US Army nearly boarded a Chinese ship after AI-hallucinated intelligence report
A US military operation nearly escalated into a major international conflict after an AI-generated intelligence report falsely claimed a Chinese vesse…

PrismML brings its tiny LLMs to Qualcomm-powered smart glasses
PrismML has announced a strategic move to deploy its specialized tiny large language models (LLMs) onto smart glasses equipped with Qualcomm processor…