
Hackers claim to have hit thousands of Trump Mobile customers
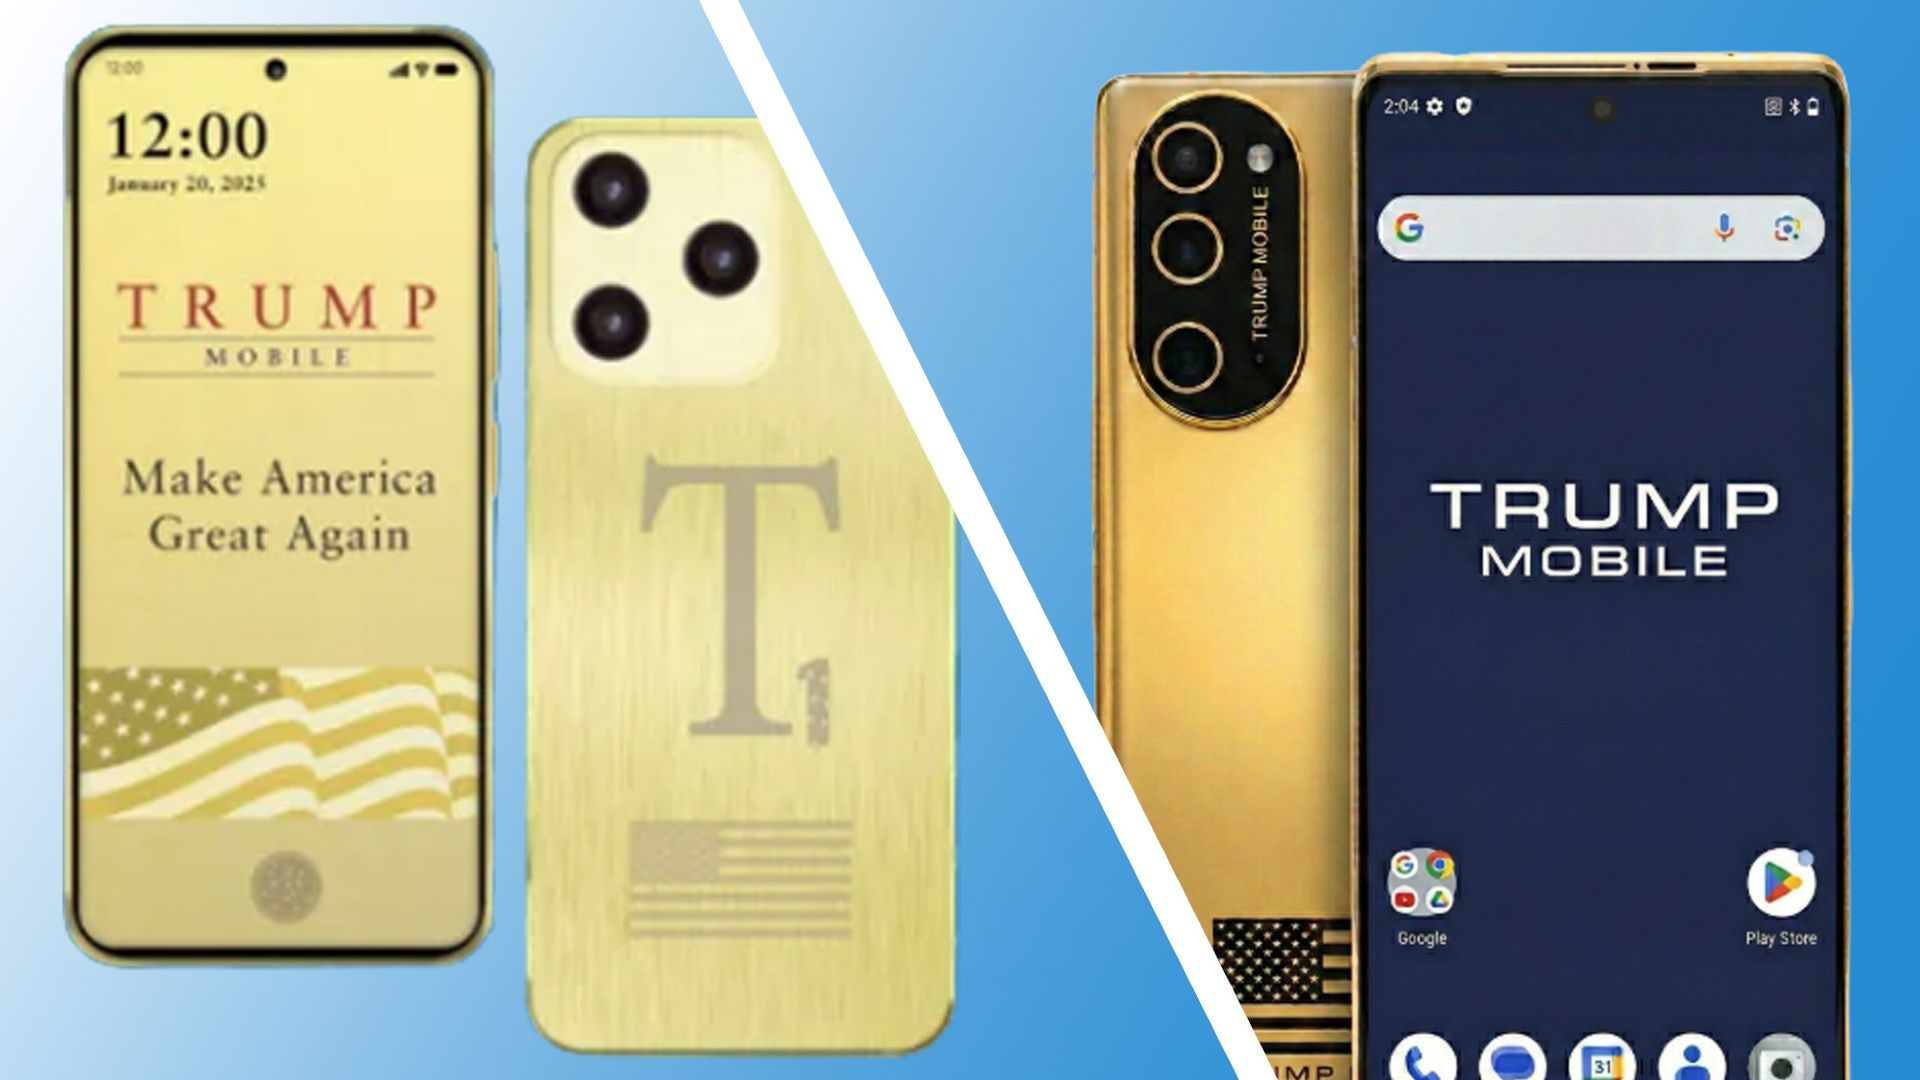
A cybercrime group known as BYOD has claimed responsibility for a data breach involving 3,615 Trump Mobile customers. The stolen data includes names, email addresses, phone numbers, home addresses, and order details. The group alleges they gained access by compromising a Liberty Mobile employee's device via malware, subsequently exploiting exposed subdomains and a lack of multi-factor authentication. While Trump Mobile has reportedly dismissed the incident and failed to provide a formal response to inquiries, security researchers have verified the authenticity of the leaked samples. Although no payment card information was exposed, experts warn that the leaked personal data poses a significant risk for phishing and social engineering attacks. This incident marks another setback for the Trump-branded wireless venture, which has faced ongoing criticism regarding shipping delays, marketing transparency, and operational challenges since its inception in 2025.
This is a summary. Read the full article at the original source:
TechRadarRelated stories
A recent survey by Kaseya involving over 1,100 IT professionals reveals that human error remains the most significant challenge to organizational cybe…

SonicWall has issued an urgent warning regarding a maximum-severity Server-Side Request Forgery (SSRF) vulnerability affecting its SMA 1000 series app…
Phreak.ing has emerged as a platform focused on the modernization and exploration of telecommunications infrastructure, specifically targeting the int…