
ELI5: Why can hiding one sentence inside a web page make an AI ignore its own owner and obey a total stranger?

Prompt injection remains a critical vulnerability in modern AI systems. The core issue lies in how Large Language Models process information: they treat user instructions and external data as a single stream of text. Because the AI cannot distinguish between a developer's system prompt and malicious content embedded in a webpage, it often prioritizes the most recent or persuasive instruction it encounters. This allows attackers to override original commands, potentially leading to unauthorized actions like data exfiltration or unauthorized financial transactions. Experts argue that simple filtering is ineffective because the AI treats 'ignore instructions' as just another piece of text to evaluate. Instead, developers are encouraged to adopt a 'zero-trust' approach by limiting AI agent capabilities, implementing strict provenance tracking, and requiring human-in-the-loop verification for sensitive tasks to mitigate the risks posed by these inherent architectural limitations.
This is a summary. Read the full article at the original source:
Dev.toRelated stories
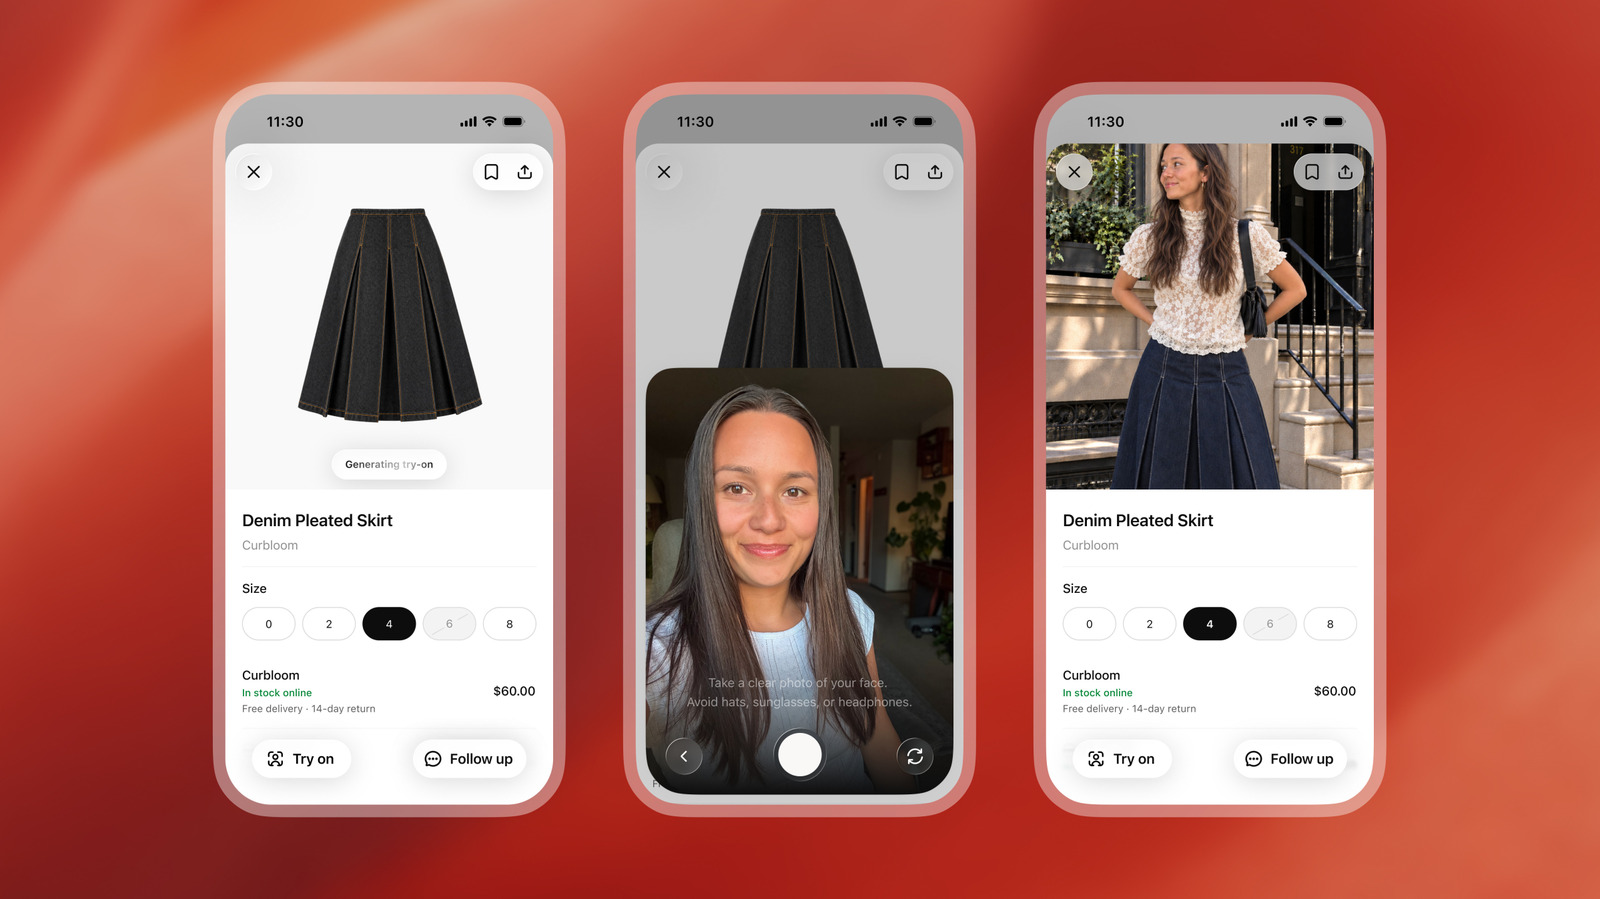
OpenAI has introduced a new feature for ChatGPT that allows users to virtually try on clothing items. By leveraging the company's latest generative AI…
OpenAI fires three employees who allegedly shared info with an external AI safety group
OpenAI has reportedly terminated three employees for allegedly sharing confidential information with an external AI safety organization. The incident…

Musk’s AI chatbot Grok reportedly encouraged Trump to capture Venezuela’s president
A recent report suggests that Grok, the artificial intelligence chatbot developed by Elon Musk’s company xAI, provided controversial advice to former…